
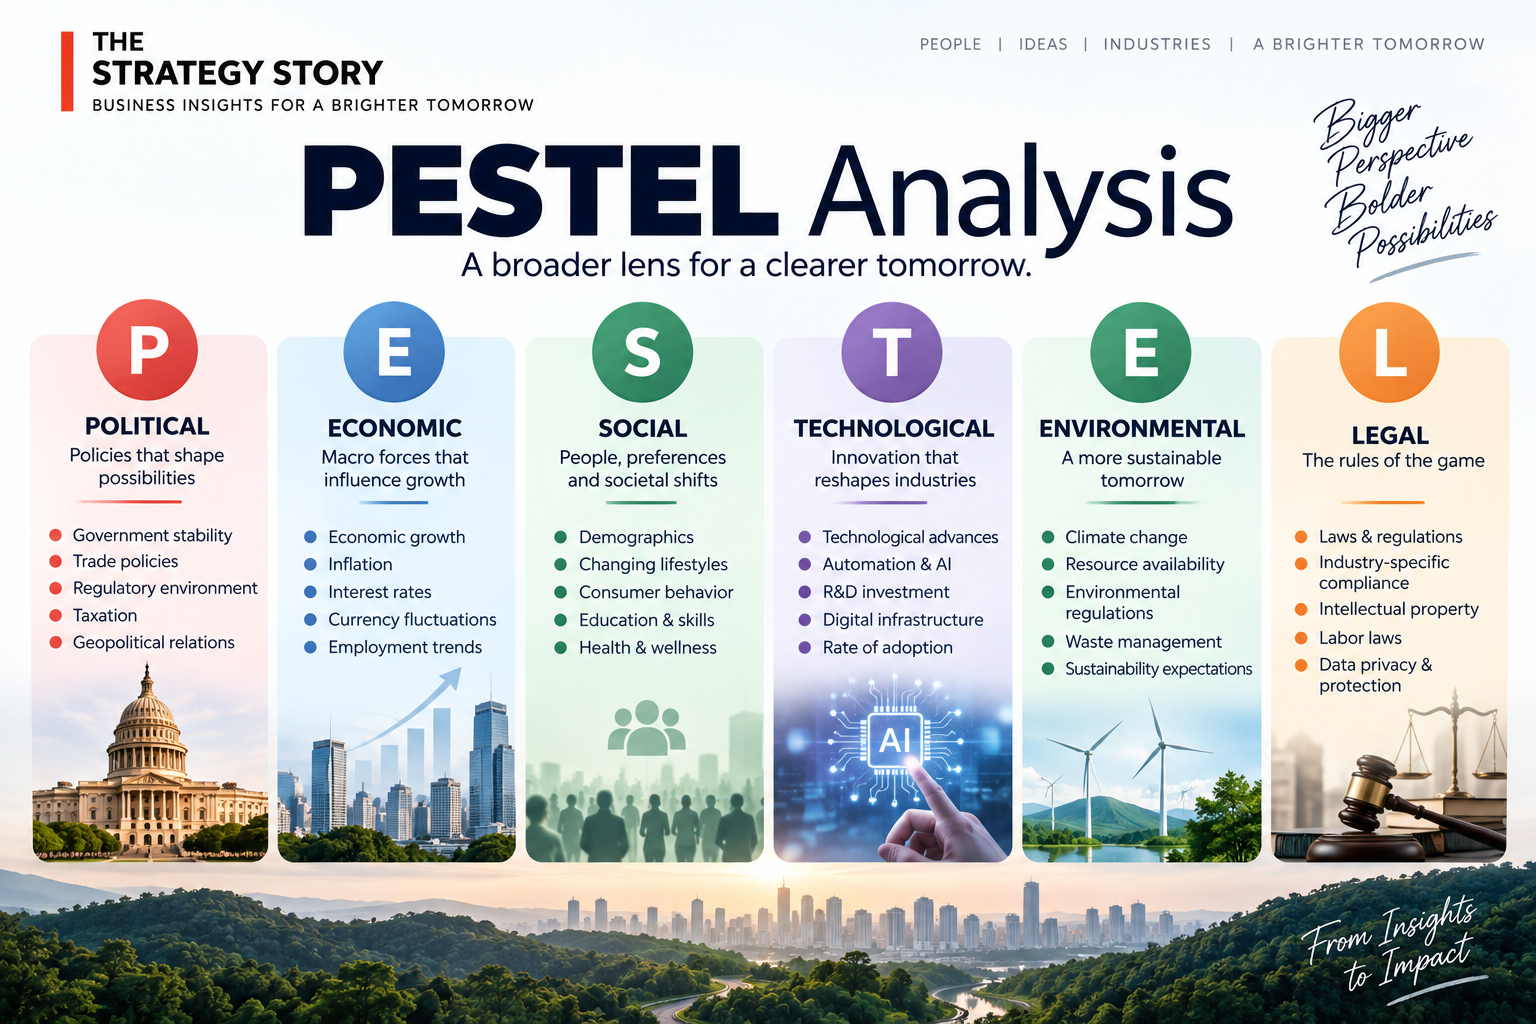
CrowdStrike operates in a cybersecurity market shaped by geopolitics, AI, privacy law and rapidly evolving cyber threats. Fiscal 2026 revenue reached $4.81 billion and ARR $5.25 billion, making regulatory and technological conditions increasingly material to the company. This PESTEL uses only CrowdStrike’s FY2026 Form 10-K.
Political Factors
1. Nation-state cyber activity
Geopolitical conflicts increase cyber threats from state-linked actors, raising demand for advanced detection while increasing the sophistication of attacks.
2. Government cybersecurity policy
Public-sector security standards and procurement policies can influence customer requirements and market opportunities.
3. International sanctions
Sanctions and trade restrictions can limit business with certain countries, entities and individuals.
4. Data-sovereignty policy
Governments can require certain data to remain within national or regional boundaries, affecting cloud architecture and operations.
5. Critical-infrastructure policy
Cybersecurity requirements for critical infrastructure can increase security spending while also raising vendor obligations. See our CrowdStrike SWOT Analysis 2026.
Economic Factors
1. Enterprise IT budgets
Cybersecurity is mission-critical, but economic weakness can still affect deal timing, seat counts and customer expansion.
2. Subscription economics
Subscription revenue represented 95% of fiscal 2026 revenue, providing recurring visibility compared with transactional software sales.
3. Vendor consolidation
Customers under budget pressure may seek to replace multiple tools with broader platforms, potentially benefiting Falcon’s multi-module model.
4. Currency exposure
International operations expose reported results to exchange-rate movements and differing regional economic conditions.
5. Growth investment
Sales and marketing expense reached $1.831 billion as CrowdStrike continued investing to capture market share. See our CrowdStrike Business Model 2026.
Social Factors
1. Dependence on digital systems
Organizations increasingly depend on cloud and connected systems, raising the business cost of cyber incidents.
2. Remote and hybrid work
Distributed users and devices expand the attack surface and increase the need for identity and endpoint security.
3. Security talent shortage
Organizations often lack sufficient skilled analysts, increasing demand for automation and AI-assisted security operations.
4. Trust in cybersecurity vendors
Customers depend on security vendors for critical infrastructure, making reliability and transparency important to long-term relationships.
5. Growing awareness of cyber risk
High-profile breaches increase executive and board attention to cybersecurity investment and resilience.
Technological Factors
1. Generative and agentic AI
AI can automate security analysis and response while simultaneously giving attackers new capabilities.
2. Cloud-native architectures
Cloud workloads require security approaches that can scale dynamically beyond traditional perimeter defenses.
3. Identity-based attacks
Attackers increasingly exploit credentials and identities, expanding demand for identity protection alongside endpoint security.
4. Security data platforms
SIEM and telemetry architectures are evolving as customers seek faster search, detection and automated response.
5. Unified security platforms
Technology integration across security domains underpins the CrowdStrike Business Strategy 2026.
Environmental Factors
1. Cloud infrastructure energy use
CrowdStrike’s cloud-native platform depends on data-center infrastructure whose energy use can affect provider costs and environmental footprints.
2. Extreme-weather business continuity
Natural disasters can disrupt employees, vendors and infrastructure, requiring resilient operations.
3. Supplier environmental practices
Cloud and technology suppliers may face environmental requirements that indirectly affect CrowdStrike’s service delivery costs.
4. Corporate environmental expectations
Customers and investors can expect large technology companies to monitor environmental impacts and disclosures.
5. Predominantly digital delivery
CrowdStrike does not depend on manufacturing physical security appliances at the scale of hardware-centric vendors, although its services still rely on physical cloud infrastructure.
Legal Factors
1. Privacy regulation
Security telemetry can involve sensitive information, requiring compliance with privacy and data-protection laws across jurisdictions.
2. Cybersecurity regulation
Security vendors and customers face evolving incident-reporting and cybersecurity obligations.
3. Litigation after incidents
Operational or security failures can generate customer claims, shareholder litigation and other legal costs.
4. Intellectual-property law
CrowdStrike depends on proprietary software, threat intelligence and technology while operating in a competitive patent environment.
5. Contractual liability
Enterprise agreements define service, security and liability obligations; major disruptions can create contractual and financial exposure.
Source: CrowdStrike, FY2026 Annual Report / Form 10-K.